The service now supports SAML configuration through the Okta Integration Network (OIN). You can add the application to Okta without configuring individual values manually.
After logging into the admin console, click [Done] on the screen below.
Confirm that the service appears in your Applications list.
Go to the [Sign On] tab and click the Edit button under Settings.
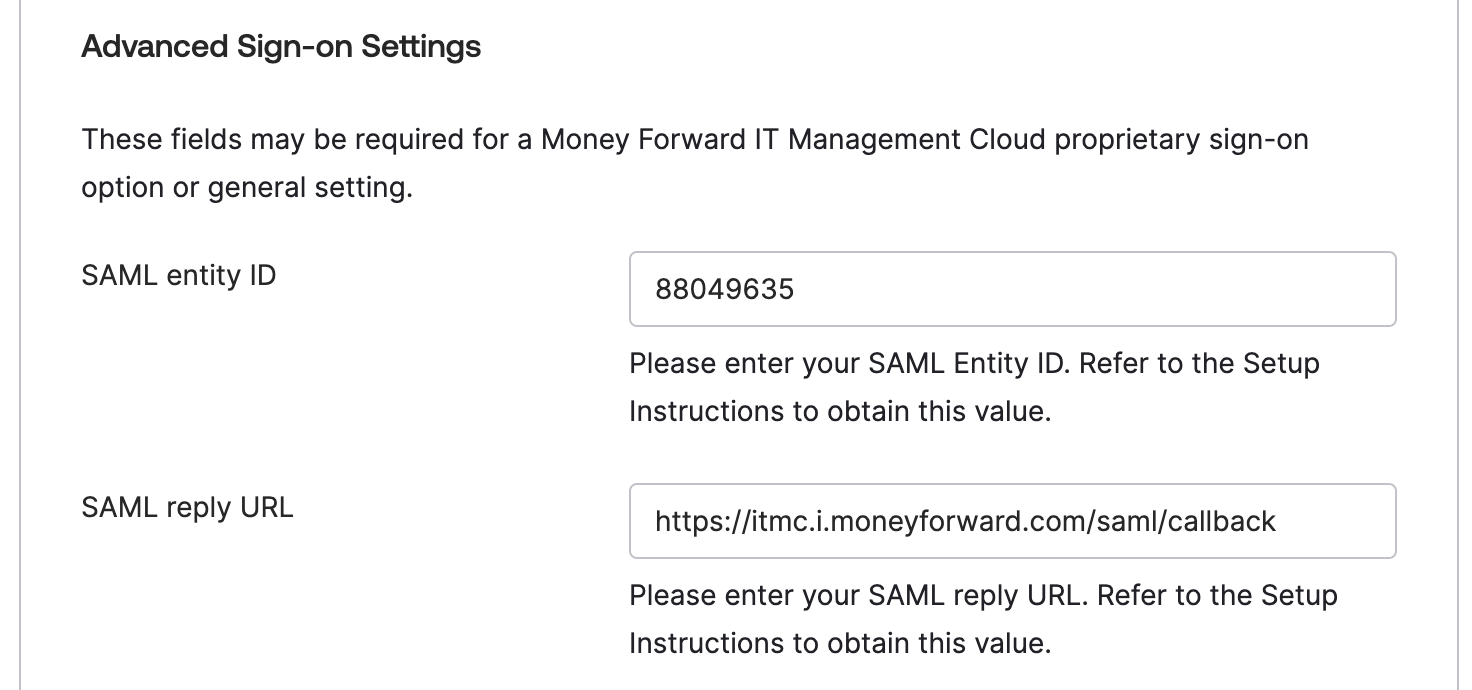
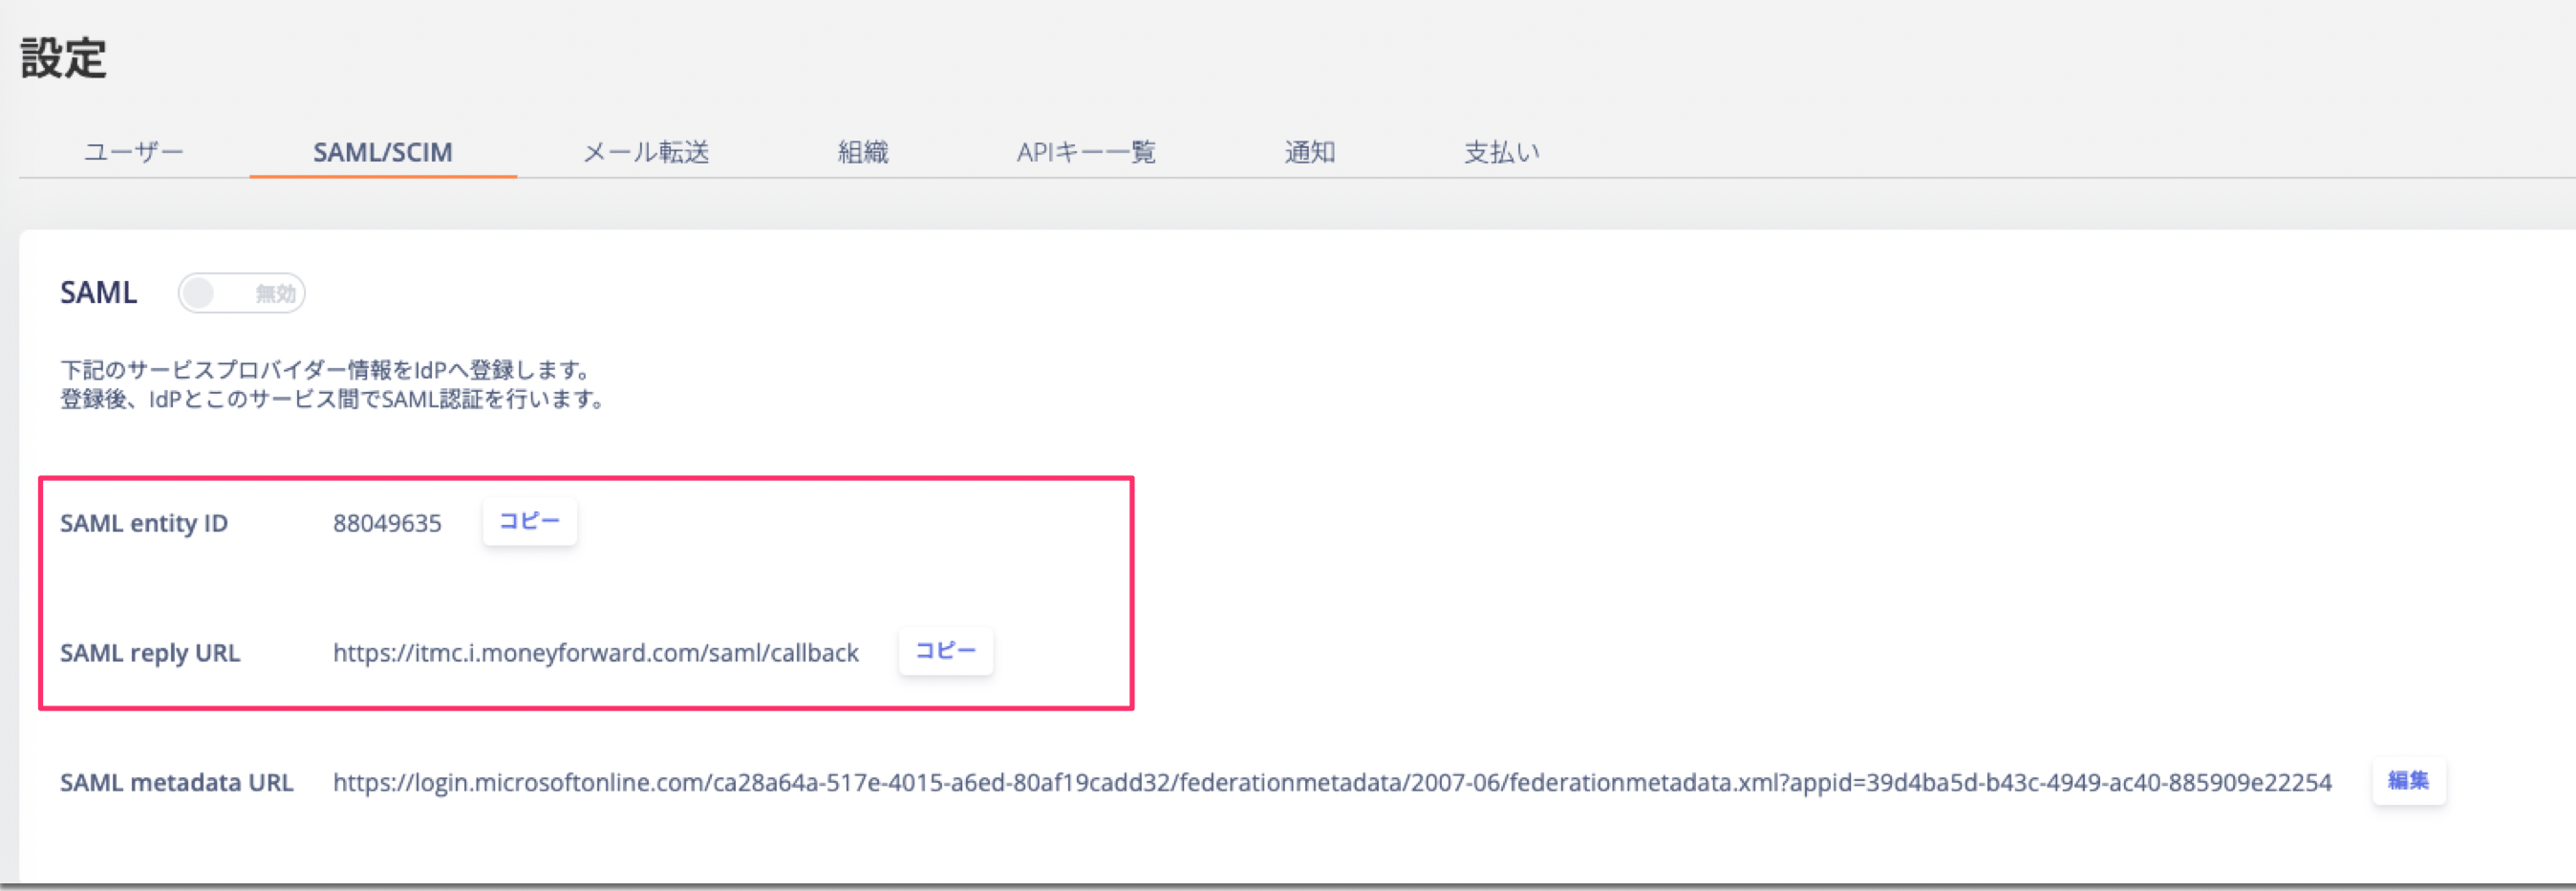
Scroll to Advanced Sign-on Settings and enter the SAML entity ID and SAML reply URL.You can find the values for SAML entity ID and SAML reply URL in the service under Settings > SAML/SCIM.
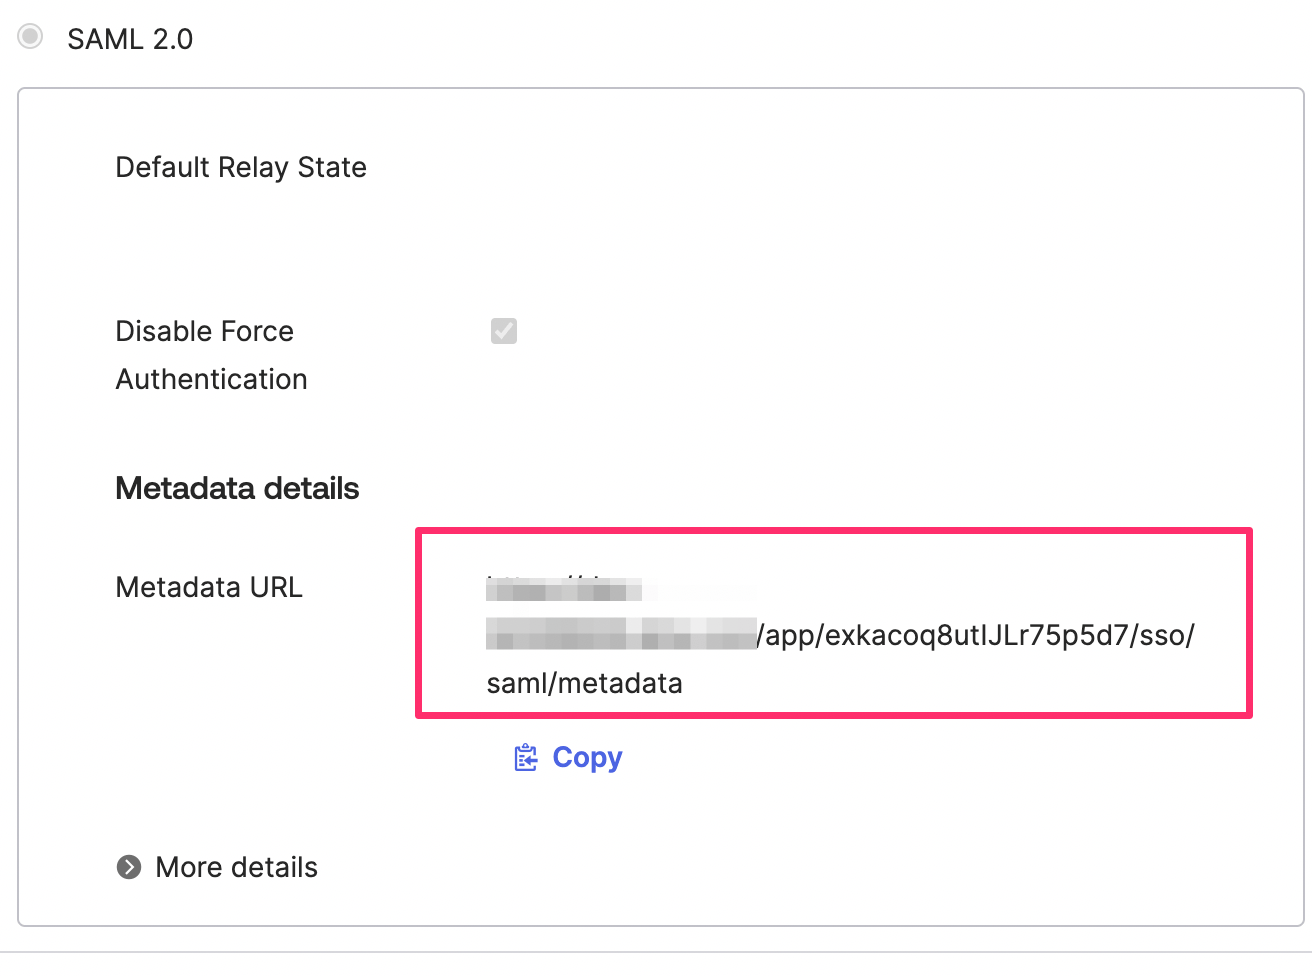
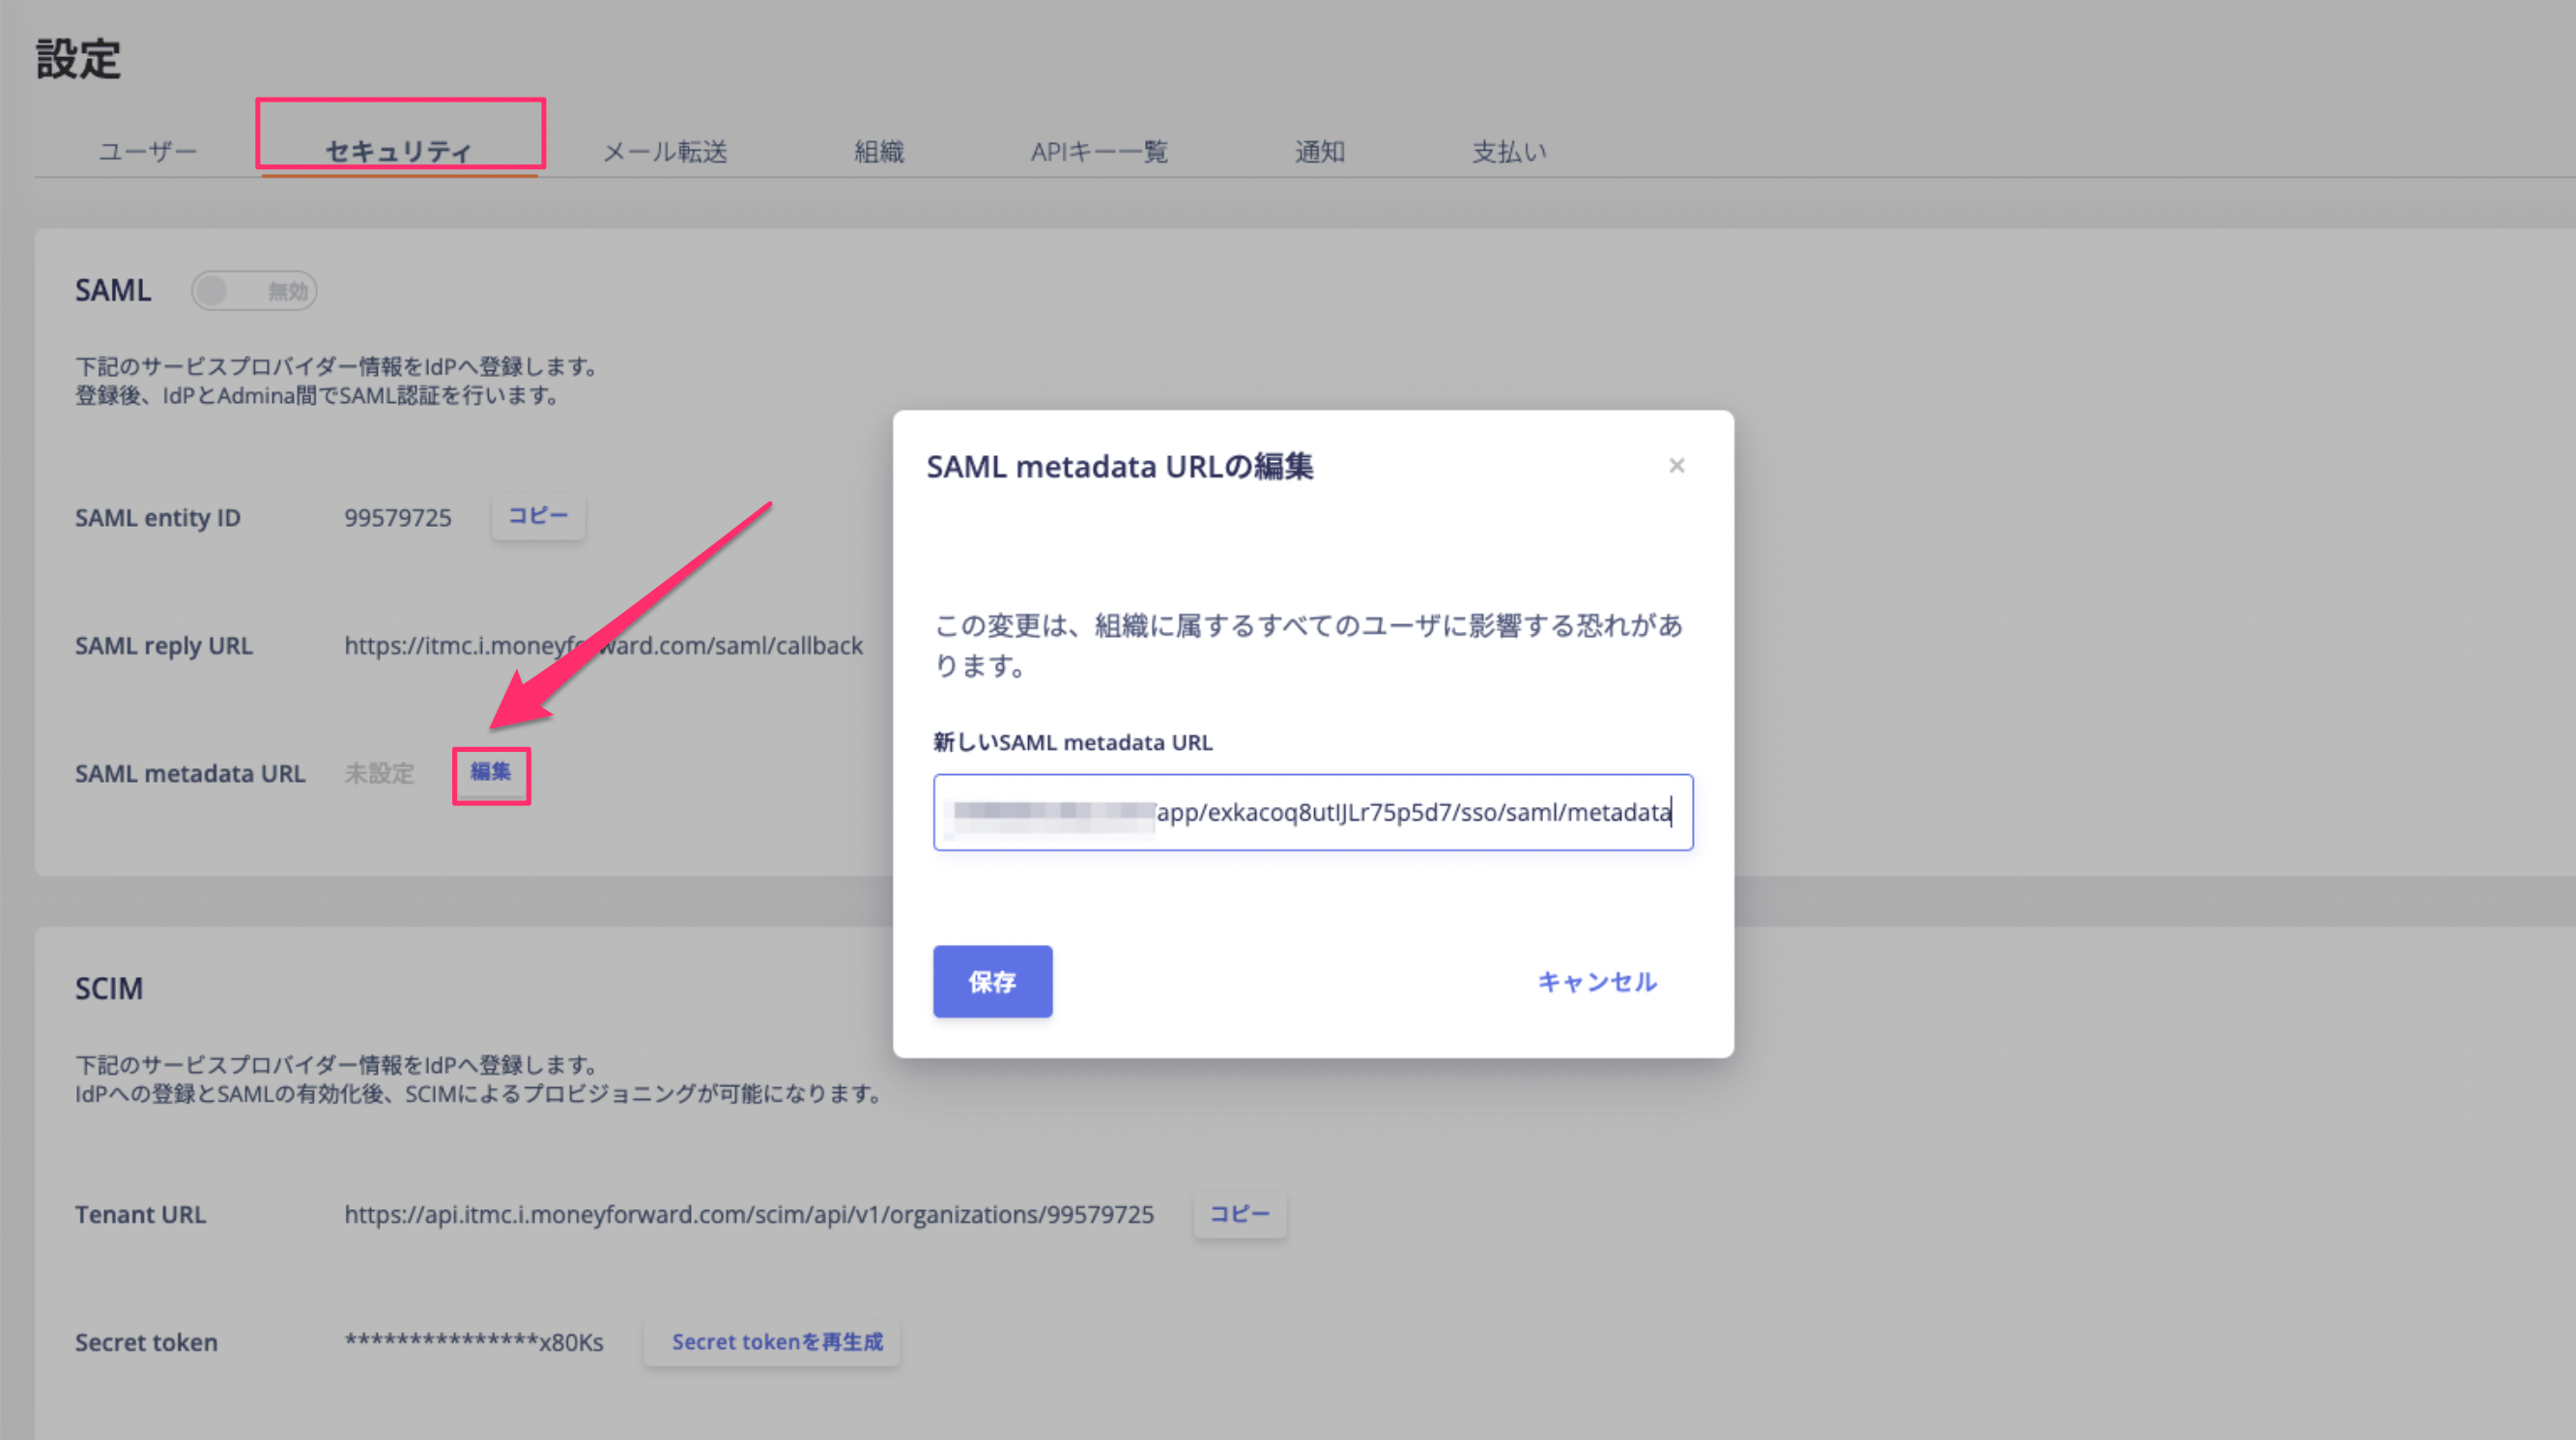
From the [Sign On] tab, copy the Metadata URL listed under SAML 2.0. Paste it into the SAML metadata URL field in the service under Settings > Security, then save.
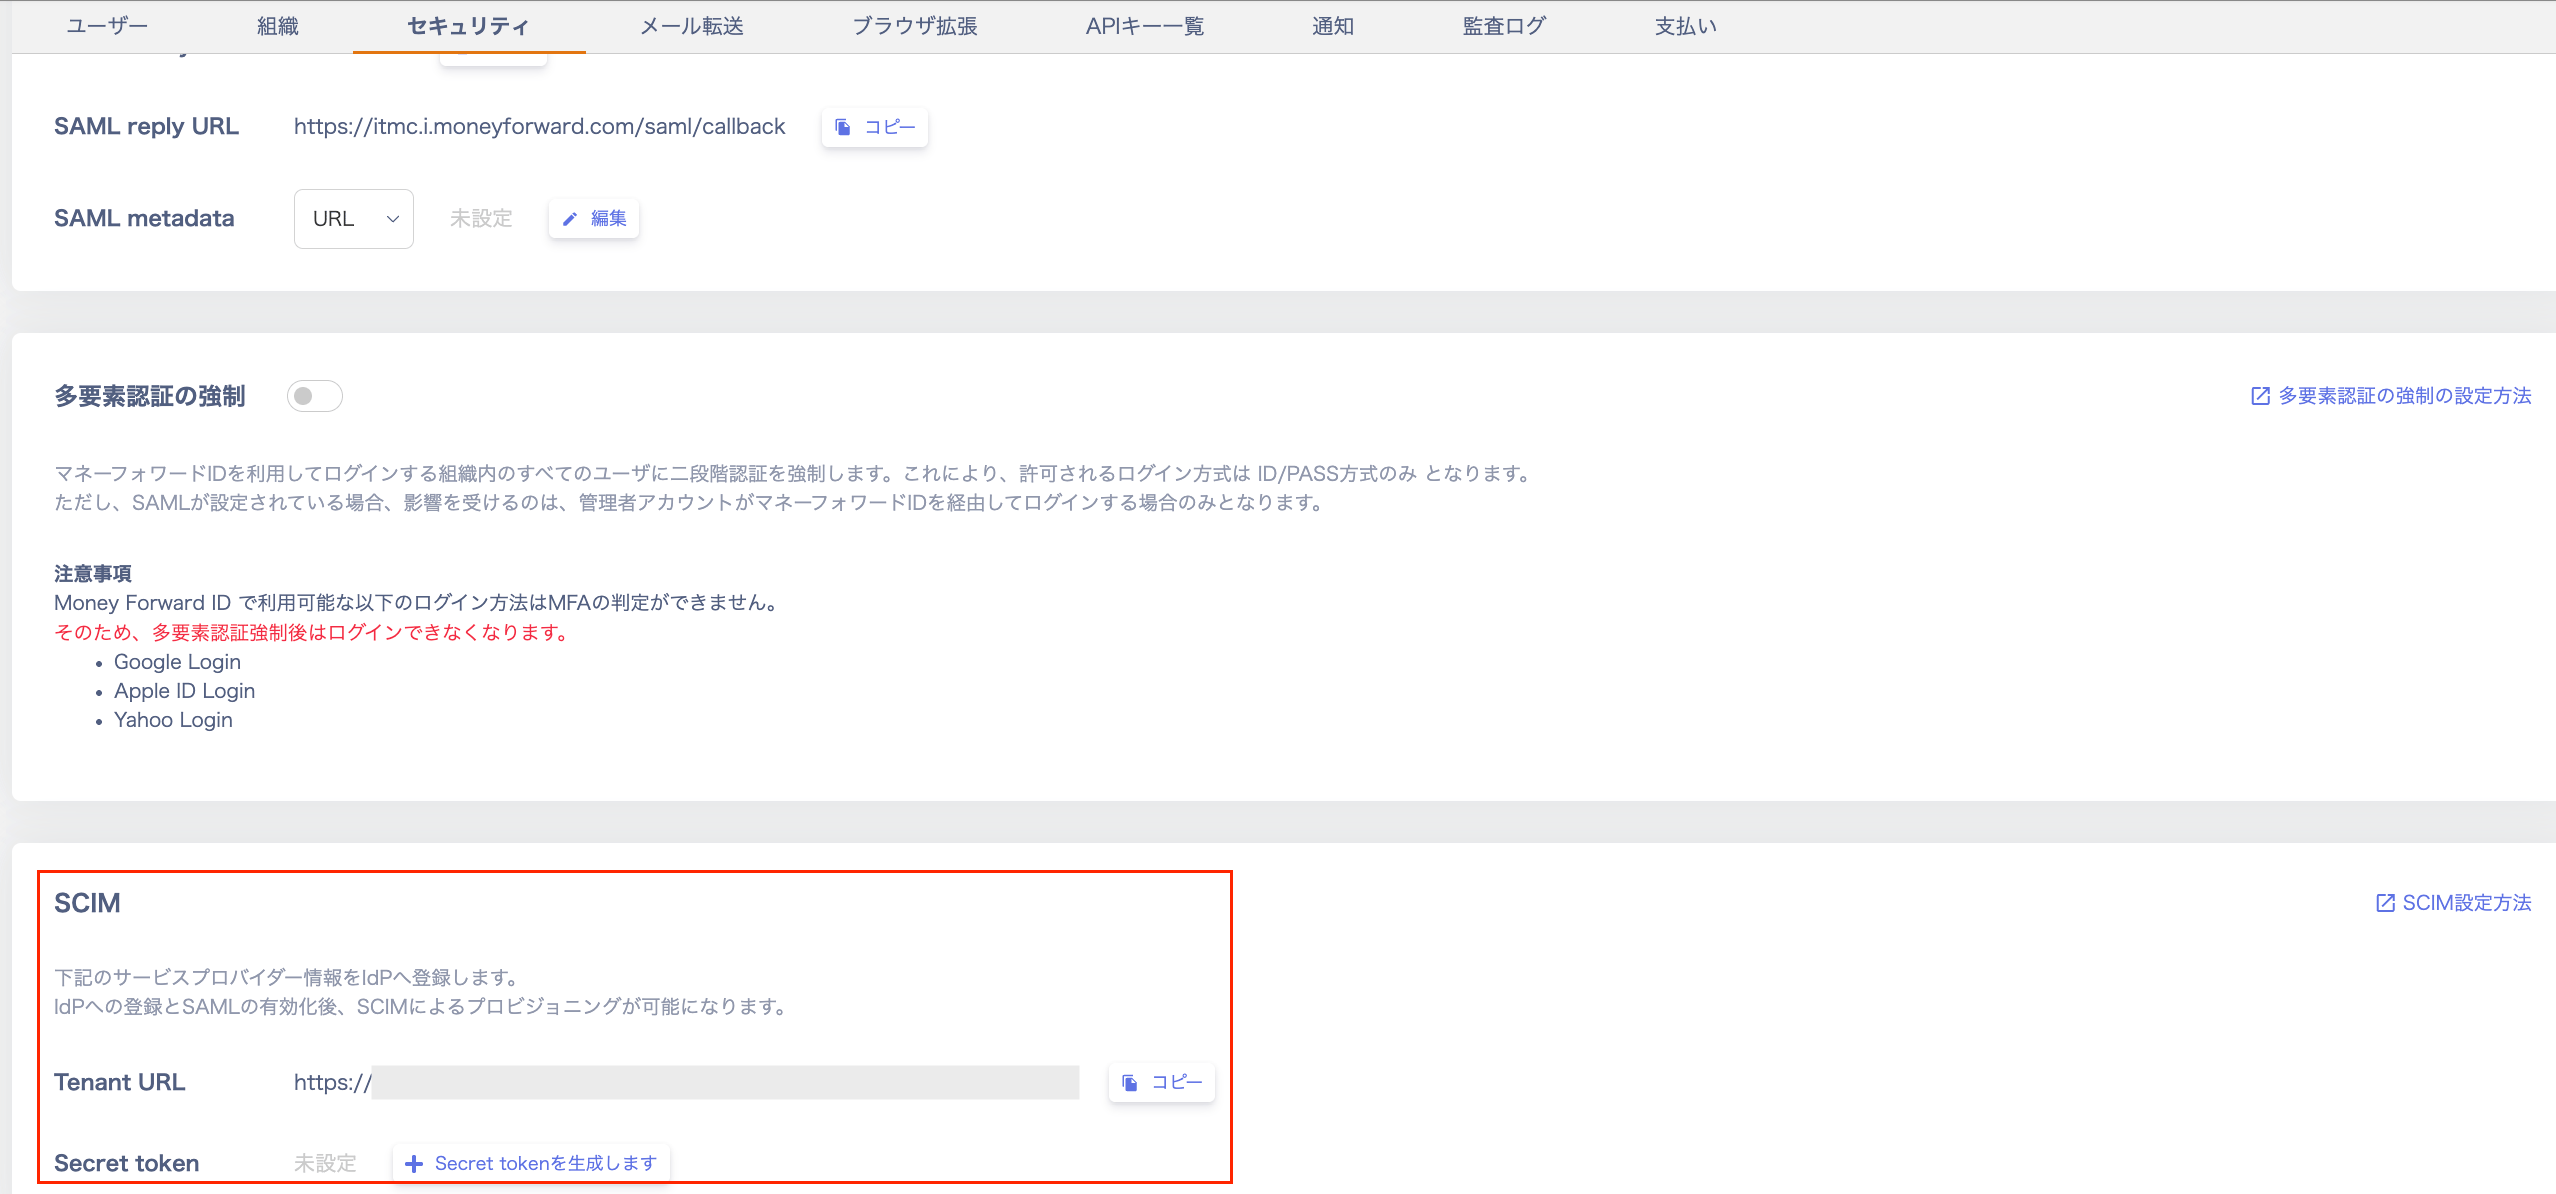
Go to Settings > Security in the service to obtain the Tenant URL and Secret Token required for IdP configuration. If no Secret Token exists, click the generate button to create one.Only one SCIM secret token is available per organization. Generating a new token invalidates the previously generated token.
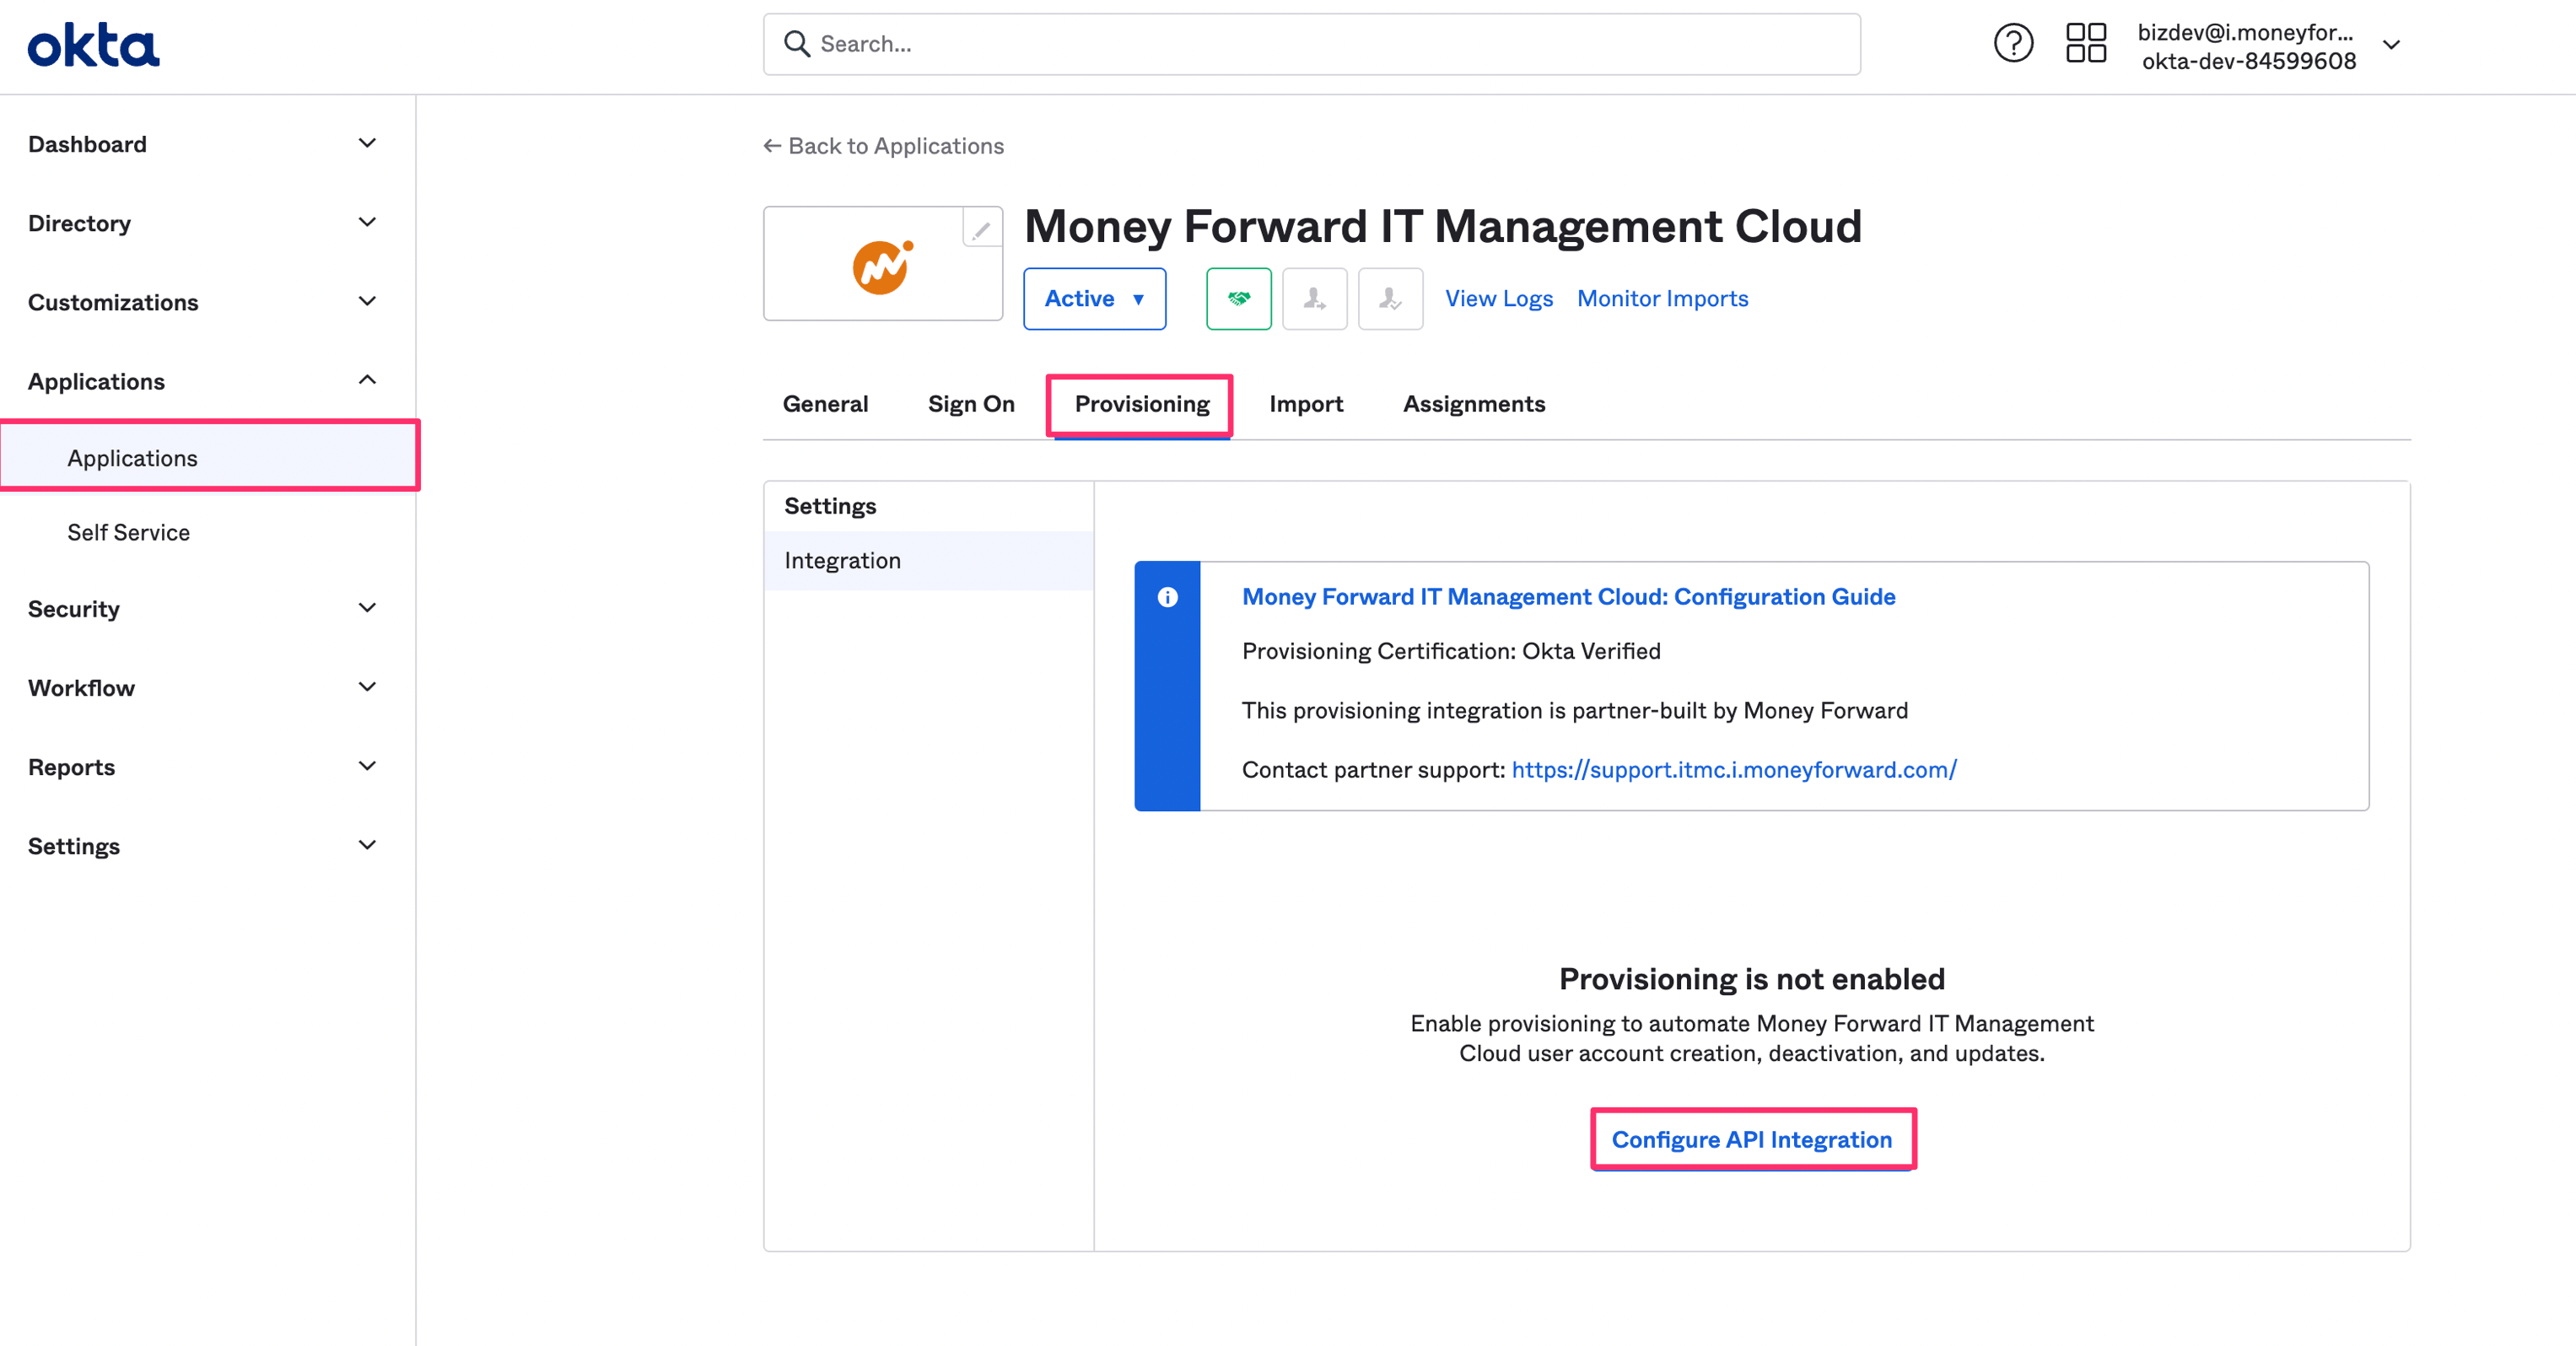
From Applications, select the application you added via OIN, then click the Provisioning tab.
Click Configure API Integration.
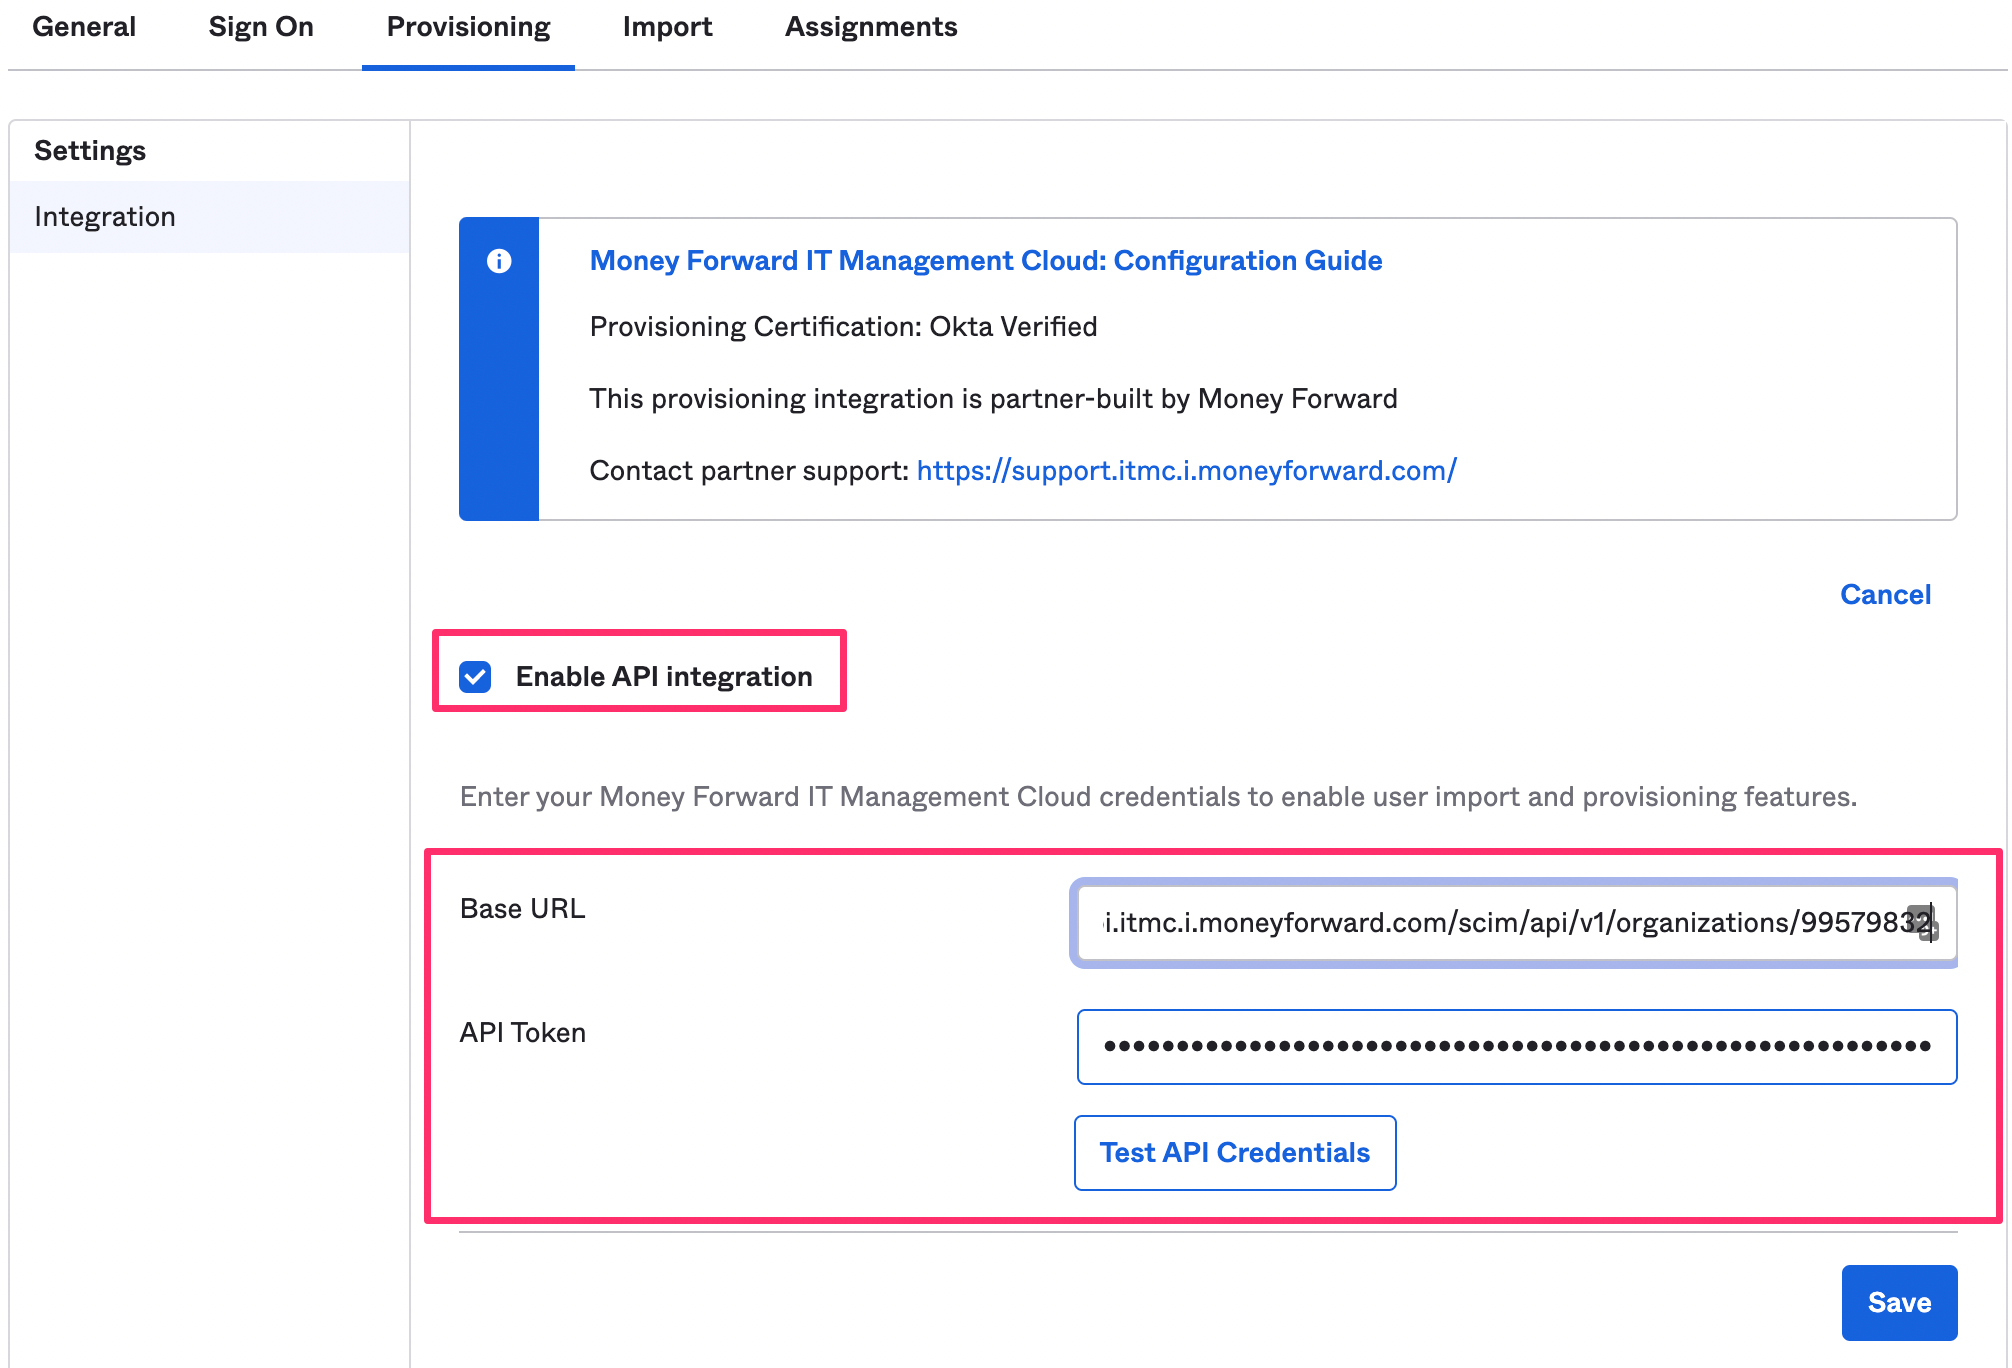
Check Enable API integration and enter the Base URL and API Token.Base URL: Enter the Tenant URL you obtained.API Token: Enter the Secret Token you obtained.
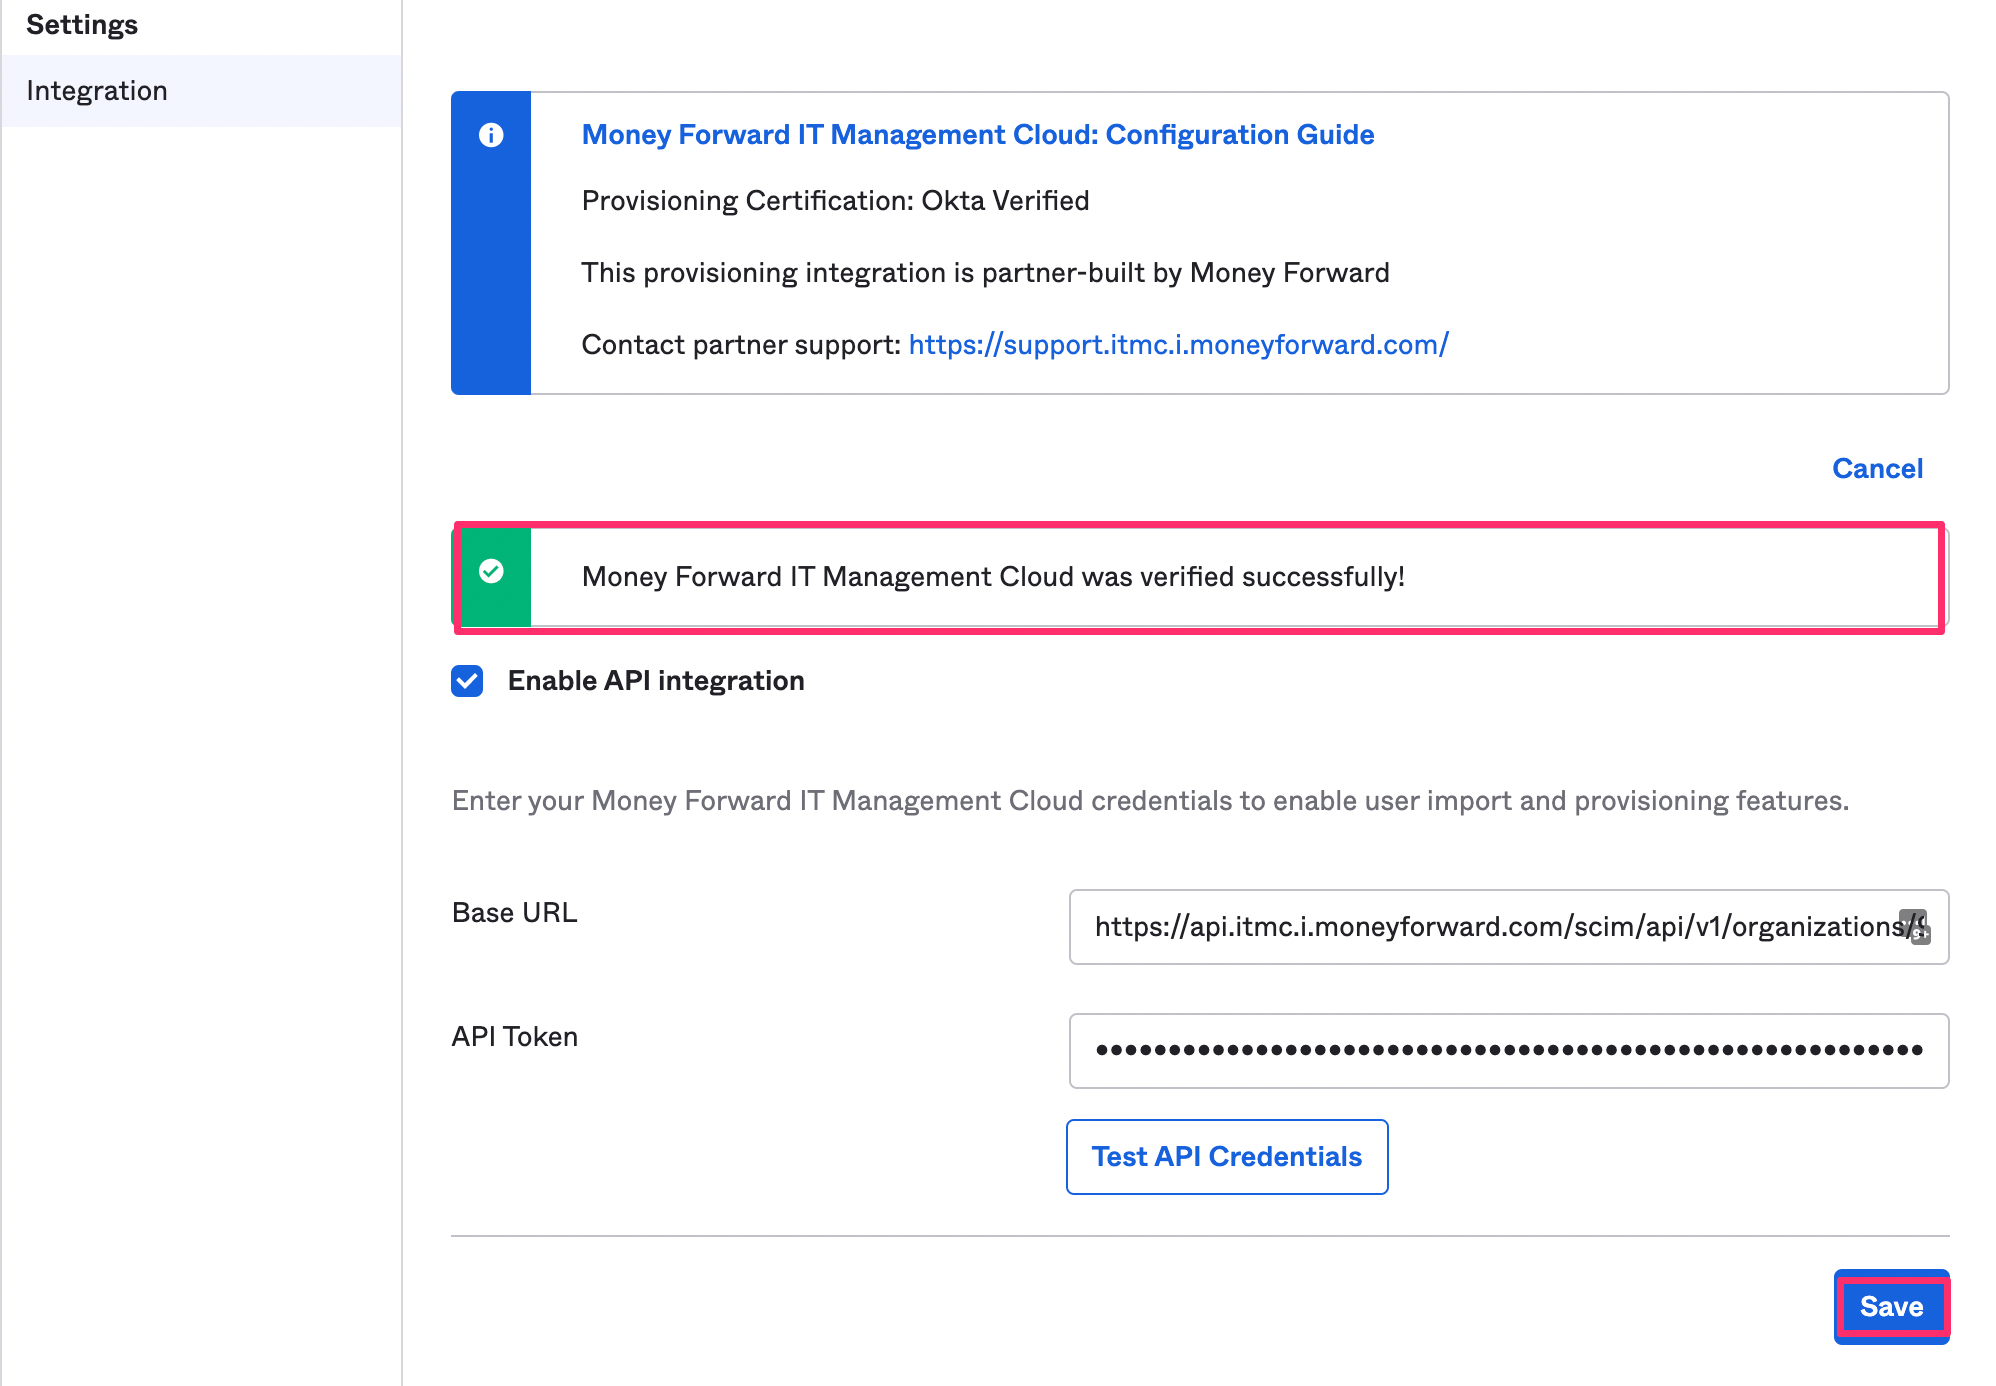
Click Test API Configuration and confirm that “the service was verified successfully!” appears. Then click Save.
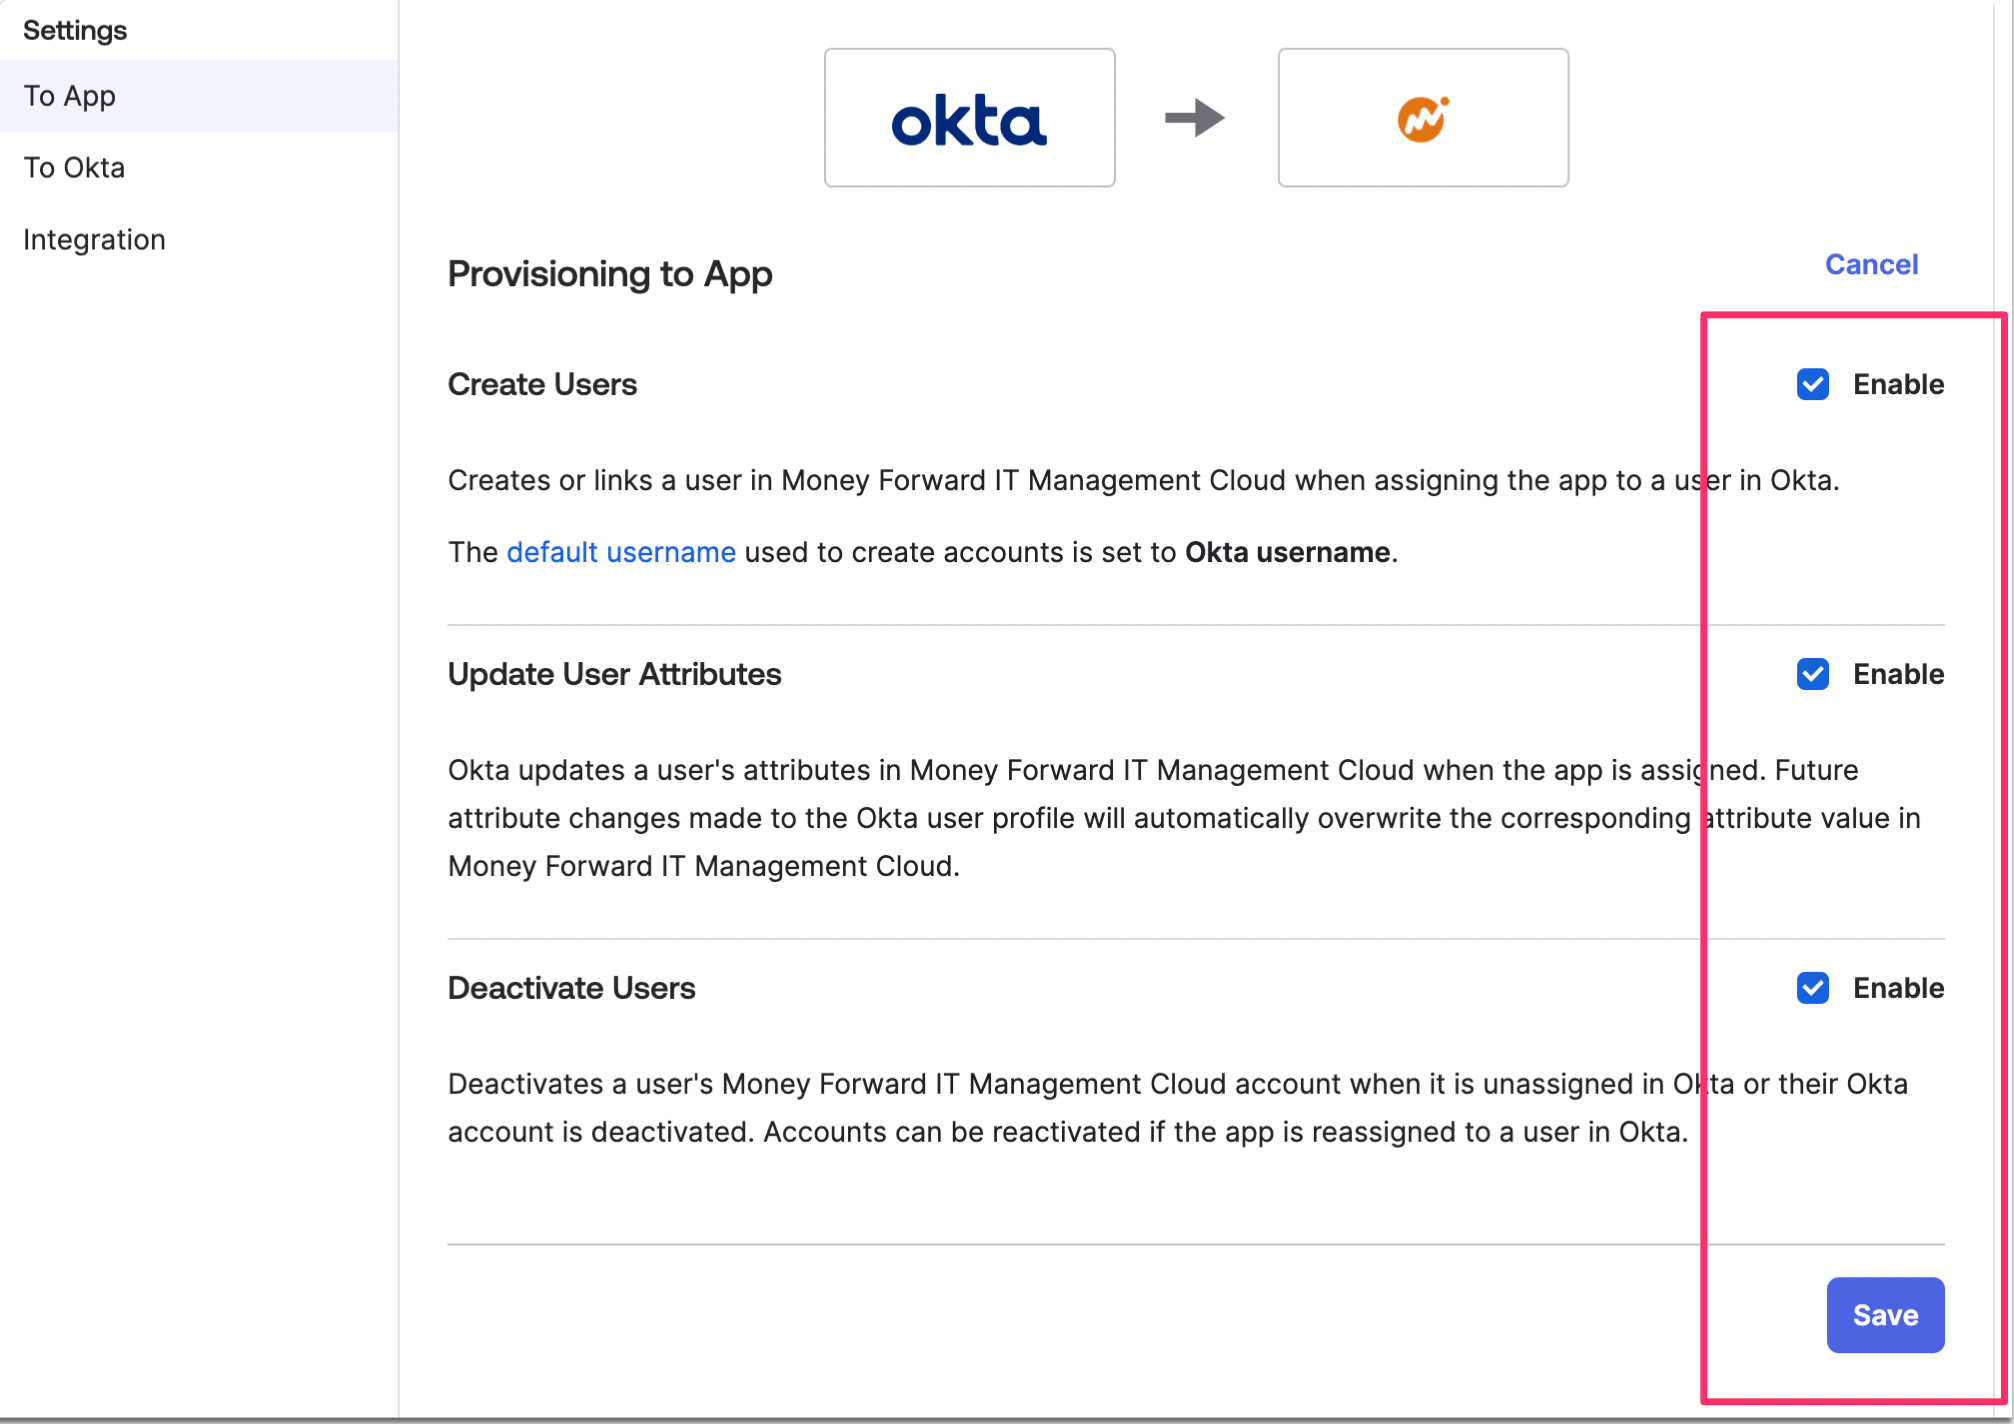
Confirm the application was added. From the To App tab, click Edit. Check Enable for Create User, Update User Attributes, and Deactivate Users, then click Save.
Setup is complete. Users assigned to the application are automatically provisioned in the service.